Last updated: November 19, 2026
Quick Answer: The fastest privacy win for most people is to change 4 settings first: app permissions, ad tracking, browser tracking protection, and account recovery options.
In short: if you want less tracking, fewer data leaks, and more control over what companies know about you, the right answer is usually to tighten settings first, then cut the data you share, then use the privacy tools already built into your phone, browser, and accounts. The keyword here is privacy.
Key Takeaways
- Privacy means controlling access, retention, and use of your data.
- Companies often request data to verify accounts, tailor services, measure use, and target ads.
- Start with app permissions, ad tracking, browser protection, and account recovery.
- Private browsing only limits local traces on your device.
I write about privacy choices, data rights, and consumer security, so I know where people get stuck: the settings are scattered, the labels are vague, and one wrong click can expose more than you meant to share. Privacy is usually won or lost in small choices, not big announcements.
This page settles the questions people ask right after they realize privacy is not a single switch.
What does privacy actually mean online?
Online privacy means control over who can see your data, how long they keep it, and what they do with it after they collect it. That includes names, emails, location data, device IDs, search history, contacts, photos, and payment details.
Picture this: you’ve signed into a shopping app, a social app, and a cloud backup account on the same phone. Each one can collect a different slice of your life, and the danger is not only hackers — it’s also routine data sharing, ad tracking, and weak account settings.
The simple version is this: privacy is about control, not secrecy. You do not need to hide everything to care about privacy. You need to limit unnecessary collection, reduce exposure, and keep sensitive data from spreading across systems that do not need it.
A lot of people mix up privacy with security. They are related, but not the same. Security keeps others out; privacy decides what gets collected in the first place.
- Privacy question: “Who can use my data?”
- Security question: “Can someone break in?”
- Good practice: reduce collection, then lock down access.
The practical starting point is the device and account you use every day. If your phone, browser, and main email account are careless with data, the rest of your privacy work has a weak base.
Why do companies ask for so much personal information?
Companies ask for so much personal information because data helps them verify accounts, personalize services, measure use, and sell or target ads. Some requests are necessary. Many are not.
Picture this: you open a new app and it asks for contacts, location, photos, microphone access, and calendar access before you’ve done anything useful. That is a red flag if the app’s core job does not need those permissions.
The real question is not “Do they ask?” It is “Do they need it?” A notes app usually does not need your contacts. A flashlight app does not need your location. A delivery app may need an address, but not permanent access to your microphone.
Here’s the catch: some data requests are hidden in the fine print rather than the permission pop-up. A company may still track you through analytics, third-party ads, or account matching even if you deny one permission.
- Needed data: shipping address, email for login, payment info for checkout.
- Usually optional: contacts, precise location, calendar, microphone, photo library.
- Red flags: forced consent, vague privacy policy, broad “partners” language.
If a service only works when you hand over far more than it needs, that service has a privacy cost. Sometimes that trade-off is worth it. Sometimes it is not.
What privacy settings should I change first?
The first settings to change are app permissions, ad tracking, browser tracking protection, and account recovery options. Those four changes do more than most people expect because they close common doors where data leaks out.
Because your phone is already full of apps, each one may touch a different part of your life. You do not need a full reset. You need a short list of high-impact changes that cut the biggest risks fast.
Start with the obvious ones:
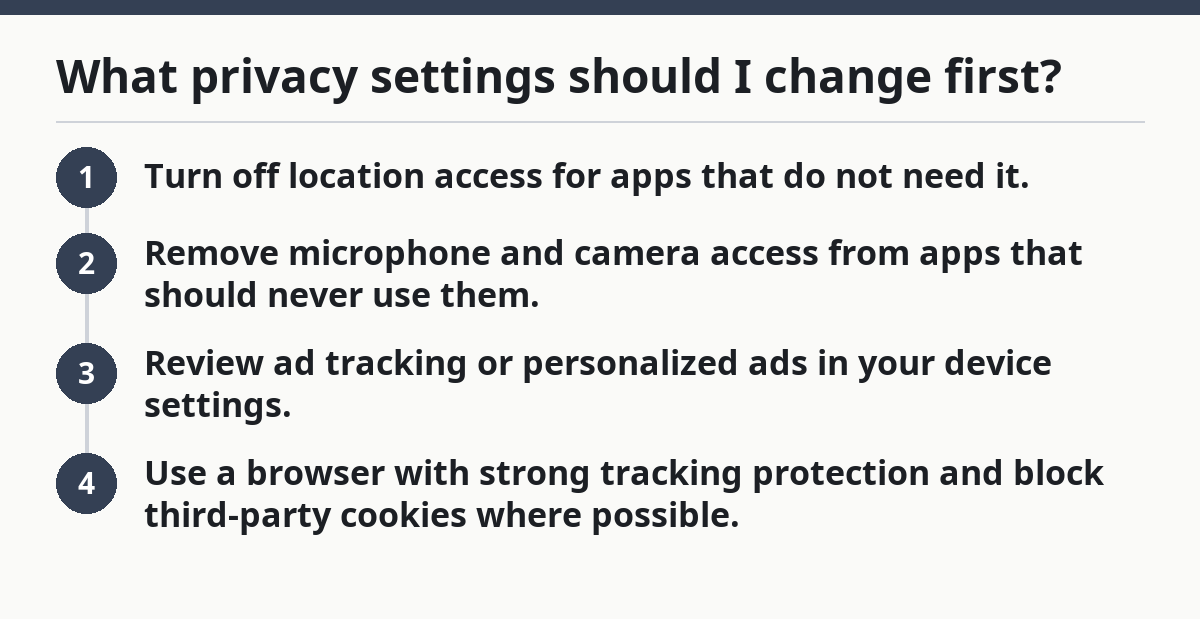
- Turn off location access for apps that do not need it.
- Remove microphone and camera access from apps that should never use them.
- Review ad tracking or personalized ads in your device settings.
- Use a browser with strong tracking protection and block third-party cookies where possible.
Then check account safety. Use a password manager, turn on two-factor authentication, and make sure your recovery email and phone number are current. An account with weak recovery settings can be stolen even if the password is strong.
If you use iPhone, Android, Chrome, Safari, or Firefox, the exact menu names differ, but the goal is the same: reduce collection, reduce sharing, reduce surprise.
For a general reference, the U.S. Federal Trade Commission’s consumer privacy advice and the Electronic Frontier Foundation’s privacy guides both explain practical steps in plain language. The FTC also notes that privacy and security overlap, but they are not identical concerns.
Is private browsing actually private?
Private browsing is only private on your device, and only in a limited way. It usually stops the browser from saving local history, cookies, and form data after you close the window, but it does not hide your activity from your internet provider, employer, school, or the sites you visit.
Picture this: you open a private window and think you are invisible. You are not. The website still sees your IP address, the network can still log traffic, and files you download can still stay on the device unless you delete them.
That is why private browsing is useful, but narrow. It helps when you do not want someone else using the same device to see your search history. It does not make you anonymous.
Use private browsing for:
- Shared computers
- Gift shopping
- Logging into a second account
- Avoiding local history on a family device
Do not use it as a shield against:
- Your internet provider
- Workplace monitoring
- Tracking by the website itself
- Malware or phishing
It is still worth using for everyday cleanup, especially on shared devices. Just do not confuse “less local evidence” with “real privacy.”
What is the difference between privacy and security?
Privacy decides how your data is collected and shared; security decides how that data is protected from unauthorized access. You need both, but one does not replace the other.
Picture this: you use a service with strong encryption and a long password, so outsiders cannot get in easily. That is security. But the service may still collect your location, contacts, and browsing behavior in the background. That is a privacy issue.
A lot of people focus on security because it is easier to picture a thief than a tracker. Still, a secure service can be invasive, and a privacy-friendly service can be badly protected. In practice, both matter, and experts generally advise addressing both. The balance depends on the risk. The safest case is to improve both. The riskiest case is to focus on one while ignoring the other.
The difference shows up in plain examples:
- A password manager with two-factor authentication improves security.
- A browser that blocks trackers improves privacy.
- A cloud app with end-to-end encryption can do both, depending on how it handles metadata.
- A social app with strict login rules may still profile you heavily.
The right fix depends on the risk. If you are worried about account takeover, strengthen security. If you are worried about profiling, reduce data collection.
Which privacy tools are worth using?
The most useful privacy tools are a password manager, a tracker-blocking browser, a two-factor authentication app, and a reputable messaging app with strong encryption. Those tools cover the most common weak spots without making daily use miserable.
Because you want better privacy without adding too much friction, the practical move is to choose a few tools that solve real problems, not every problem.
A password manager helps because it lets you use unique passwords without memorizing them all. A tracker-blocking browser helps because it cuts ad networks and third-party scripts that follow you around the web. A two-factor app helps because stolen passwords alone are less useful. An encrypted messaging app helps because some conversations should stay out of ordinary SMS or social feeds.
That said, every tool has trade-offs:
- Password managers become a high-value target, so the master password and recovery setup matter.
- Tracker blockers can break some sites or make logins annoying.
- Two-factor apps can lock you out if you lose your device and ignore recovery codes.
- Encrypted messaging only helps if the other person uses it too.
If you want a trustworthy source list, look at guidance from the Electronic Frontier Foundation and the UK Information Commissioner’s Office. Both explain the basics without pretending privacy is magic.
When should I worry most about privacy?
You should worry most about privacy when you share sensitive data, use a shared device, install unknown apps, or connect to public networks. Those are the moments when a small mistake can spread fast.
Picture this: you are at a café, signing into email on public Wi‑Fi, checking a bank alert, and installing a new app because it looks useful. That is not paranoia territory — that is normal life, and it is exactly where bad privacy habits show up.
The highest-risk moments are predictable:
- Logging into accounts on someone else’s device
- Granting broad permissions to new apps
- Reusing passwords across services
- Posting location-heavy photos in real time
- Filling out forms on sites you do not trust
The fix is usually simple. Wait before you post. Read the permission prompt. Use a secure connection, and if you are unsure about the safest option for your situation, consult a qualified professional or your organization’s IT or security team. Keep sensitive accounts behind two-factor authentication. And if a service asks for more than it needs, say no.
This is also where “privacy” and “judgment” meet. A perfect settings screen will not save you if you hand over the wrong data at the wrong time.
What should I do if my privacy has already been exposed?
If your privacy has already been exposed, change the password, review account activity, revoke unknown sessions, and remove any permissions you do not trust. If the exposure involves money, identity, or a workplace account, act fast and keep records.
Picture this: you notice a login alert from a city you have never visited, or an app has been using your location more than you expected. The first job is not panic. The first job is containment.
Start here:
- Change the password on the affected account.
- Turn on or reset two-factor authentication.
- Sign out of other devices or sessions.
- Check recovery email and phone settings.
- Review linked apps and connected devices.
- Watch for follow-up emails, charges, or login alerts.
If the exposure touches financial data or a government account, contact the relevant institution directly and follow its fraud or identity-theft steps. For broad guidance, the FTC and your local consumer-protection agency are good starting points.
The Verdict: Which privacy question matters most?
The most important privacy question is not “Can I disappear online?” It is “What data should this service really have, and what can I cut back right now?” That question leads to action instead of anxiety.
Choose tighter app permissions if you use a phone full of apps and want the fastest risk reduction. Choose stronger account security if your biggest fear is account takeover. Neither helps much if you keep handing out data to services that do not need it.
FAQ
How do I know if an app is too nosy?
An app is too nosy if it asks for access that does not fit its job. A calculator does not need contacts, and a simple note app usually does not need your microphone or precise location. If the permission request feels out of place, it probably is.
Does deleting an app remove my data?
Not always. Deleting an app from your phone does not always delete the account, the cloud copy, or the data the company already stored. Check the app’s account settings and privacy policy if you want the data gone too.
Is a VPN the same as privacy?
No. A VPN can hide your traffic from your internet provider and change the network path, but it does not stop the website itself from collecting data. It is one tool, not a full privacy plan.
Are privacy policies worth reading?
Yes, but read the parts that matter: what data they collect, who they share it with, how long they keep it, and how to delete it. The useful answer is usually in those sections, not in the legal flourishes.
What is the fastest privacy win for most people?
Turning off unnecessary app permissions is the fastest win for most people. It cuts routine data sharing without breaking your daily life, and it takes less time than setting up a whole new system.
Drafted with AI; not yet reviewed by a person.